


Cyber Resilience Act: Your Analysis
Reduce project, compliance, and market risk before hidden gaps turn into late, expensive changes. IMT engineers review your existing product and process documentation and show you what already meets the Cyber Resilience Act, what's missing, and where to start.
Waiting won't make it any cheaper.
Most companies don't actually know where they stand on the Cyber Resilience Act — so the review keeps getting pushed back. The risk: gaps surface late, often right before a major milestone, when fixes cost far more than they would have earlier. The CRA Analysis gives you clarity within a week, before that pressure builds.
The CRA is an EU regulation covering products with digital elements. It sets binding cybersecurity requirements to reduce the risk of cyberattacks across the market. Reporting obligations take effect on 11 September 2026; the remaining core obligations follow on 11 December 2027. Read more on the IMT expert blog.

One specific product. No black-box guesswork.
We analyze one clearly defined device, system, or software product — including every digital component relevant to how it functions and how secure it is.
- Likely CRA applicability, and the assumptions behind it
- An initial read on product category and conformity path
- Product and system architecture, interfaces, and security-by-design choices
- Security requirements and evidence against the CRA's core requirements
- How vulnerabilities, updates, support, and incidents are handled
- Software composition, including your SBOM
- Development, change, configuration, and vulnerability-management processes
- Technical documentation and how traceable your security decisions are
Not a report to file away — a foundation for decisions.
Five concrete results, plus a personal conversation.

Executive Summary
A management-ready summary of where you stand, the main risks, and what to do next.

Applicability & classification assessment
A reasoned first read, with the assumptions and open questions spelled out.

CRA gap overview
Requirements, existing evidence, and identified gaps, laid out side by side.

Prioritized recommendations
Concrete next steps for product, architecture, documentation, and process.

List of potential measures
Quick wins you can act on now, plus topics to plan for later.
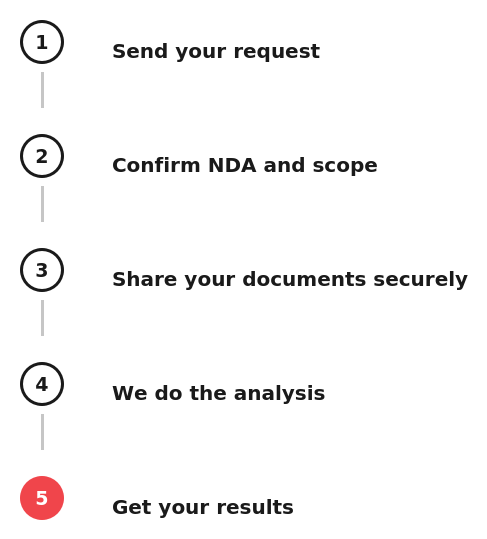
5 steps, one week
CHF 4'500. Fixed. No surprises.
Price & Timeline
CHF 4'500. Applies to one clearly named product. Technically identical variants can be included once confirmed.
Not included
Legal opinion or binding legal advice · Certification · Penetration testing or code audit · Implementing the measures · Full rewrite of the technical documentation
Engineers who already know what's at stake.
IMT has spent more than 30 years building demanding devices, embedded systems, and software. Analysis led by engineers with product development and cybersecurity experience, real experience in regulated and safety-critical development environments, and ISO 27001 certification.
Your contact
Looking for an engineering partner to get clarity on the Cyber Resilience Act? Reach out to our team and start your CRA journey.
Benno Bieri
COO & Head of Business Development

Remo Züger
Business Development Manager & Project Lead
Michael Trummer
Business Development Manager & Project Lead
Reach out to our team